educationJun 13, 202618:46pending
Course 36 - Windows Forensics and Tools | Episode 15: Uncovering Digital Evidence from Headers and Servers
About this episode
In this lesson, you’ll learn about: email forensics and how investigators trace the origin and authenticity of emails using technical artifacts and server data1. What Is Email Forensics?Email forensics is the process of analyzing emails to:
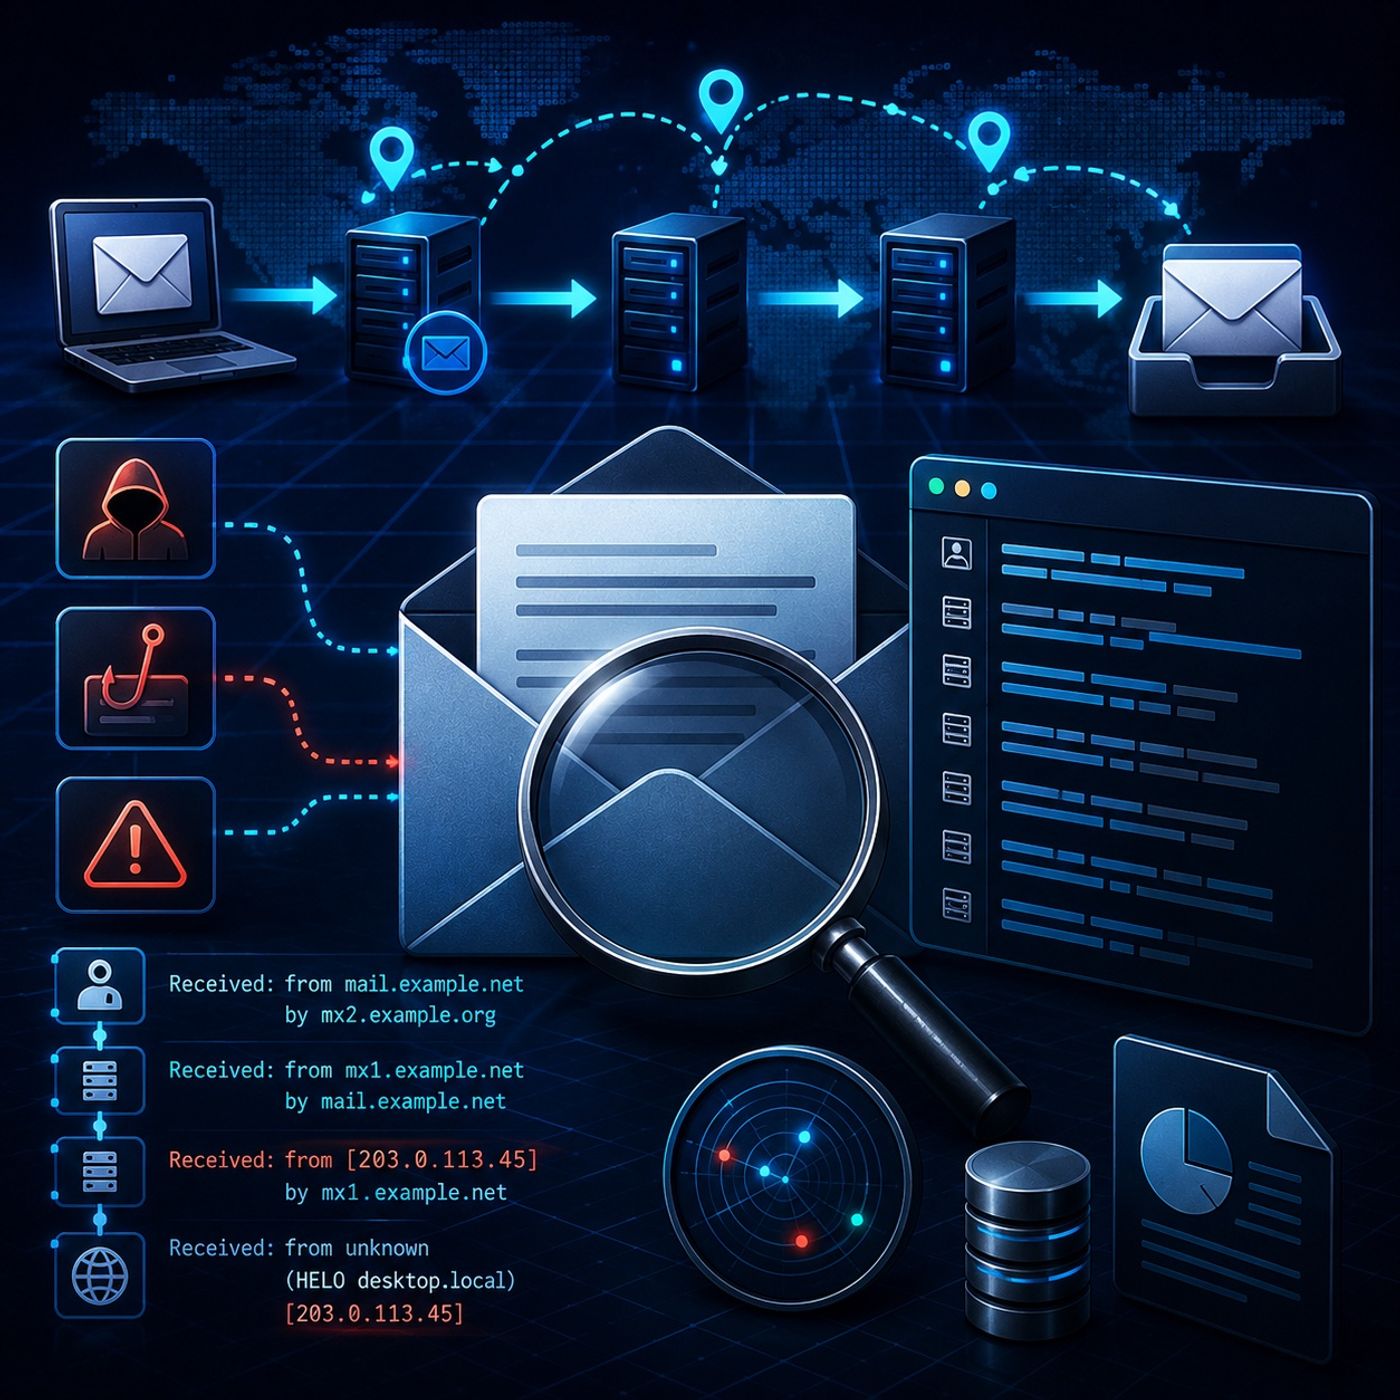
Every email leaves behind a traceable digital trail, even if the content is altered or deleted.2. Email Lifecycle (How Emails Travel)An email typically moves through several systems:
Each hop adds metadata that becomes part of the email’s permanent record.3. Email Headers (The “Gold Mine”)🔹 What email headers contain:
Headers cannot easily be faked completely, making them crucial for investigations.4. Header Analysis (Bottom-to-Top Method)Investigators analyze headers starting from the bottom:🔹 Why bottom-to-top?
This method helps uncover the true origin of suspicious emails.5. Detecting Email AttacksEmail forensics helps identify:🔹 Spoofing
Even carefully crafted malicious emails often leave traceable technical evidence.6. Supporting Evidence SourcesInvestigators also use:
Cross-checking multiple logs increases investigation accuracy.7. Forensic Tools Used in Email Analysis🔹 Common tools include:
Tools automate complex parsing but rely on human interpretation.Key Takeaways
👉 Trace communication paths across servers
👉 Prove or disprove email authenticity in cyber incidentsMental ModelEmail sent → passes through servers → headers accumulate → forensic analysis reconstructs origin and path
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
- Identify the real sender
- Detect tampering or spoofing
- Reconstruct the path an email traveled
- Gather evidence for cyber investigations
Every email leaves behind a traceable digital trail, even if the content is altered or deleted.2. Email Lifecycle (How Emails Travel)An email typically moves through several systems:
- MUA (Mail User Agent): The email client (e.g., Outlook, webmail)
- MTA (Mail Transfer Agent): Servers that route emails across the internet
- Multiple intermediate mail servers before reaching the recipient
Each hop adds metadata that becomes part of the email’s permanent record.3. Email Headers (The “Gold Mine”)🔹 What email headers contain:
- Sender and recipient information
- Server IP addresses
- Time stamps for each relay
- Authentication results
Headers cannot easily be faked completely, making them crucial for investigations.4. Header Analysis (Bottom-to-Top Method)Investigators analyze headers starting from the bottom:🔹 Why bottom-to-top?
- The bottom shows the original source
- Each line above shows the email’s path through servers
- Original sender IP
- First mail server used
- Path of email delivery
This method helps uncover the true origin of suspicious emails.5. Detecting Email AttacksEmail forensics helps identify:🔹 Spoofing
- Fake sender addresses
- Deceptive emails designed to steal credentials
- Unauthorized data sent outside an organization
Even carefully crafted malicious emails often leave traceable technical evidence.6. Supporting Evidence SourcesInvestigators also use:
- Mail server logs
- Network device logs (firewalls, proxies)
- Authentication records
Cross-checking multiple logs increases investigation accuracy.7. Forensic Tools Used in Email Analysis🔹 Common tools include:
- Email tracking and analysis utilities
- Digital forensic suites (e.g., FTK-based tools)
- Header decoding
- Attachment analysis
- Password recovery (in some cases)
- Evidence extraction and reporting
Tools automate complex parsing but rely on human interpretation.Key Takeaways
- Email headers contain the most critical forensic evidence
- Emails pass through multiple servers, each leaving traces
- Bottom-to-top header analysis reveals the original sender
- Server logs help validate email authenticity
- Tools assist, but analysis logic is what finds the truth
👉 Trace communication paths across servers
👉 Prove or disprove email authenticity in cyber incidentsMental ModelEmail sent → passes through servers → headers accumulate → forensic analysis reconstructs origin and path
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
Get every episode summarized
Each time CyberCode Academy publishes, we email you a written briefing from the transcript — the topics, who appeared, and any specific claims, with the ad reads skipped.
Email me new episodesFree for 3 shows. No card needed.
Hosts & guests
No transcript yet
This episode has not been transcribed. Request it and it moves to the front of the queue.
More episodes
More from CyberCode Academy

Course 42 - Mobile Malware Analysis Fundamentals | Episode 14: Architecture and...
CyberCode Academy
Sep 10, 202624:31completed

Course 42 - Mobile Malware Analysis Fundamentals | Episode 13: Designing and Arc...
CyberCode Academy
Sep 9, 202617:34failed

Course 42 - Mobile Malware Analysis Fundamentals | Episode 12: Dynamic Analysis...
CyberCode Academy
Sep 8, 202628:08completed

Course 42 - Mobile Malware Analysis Fundamentals | Episode 11: Dynamic Analysis...
CyberCode Academy
Sep 7, 202624:15completed